Spend less time administering compliance. Keep control of the work.
Bring approvals, staff declarations, deadlines and evidence into one workspace. Reduce follow-up emails and repeated data entry, review requests with the facts in view, and find the records you need without rebuilding the story from inboxes and spreadsheets.
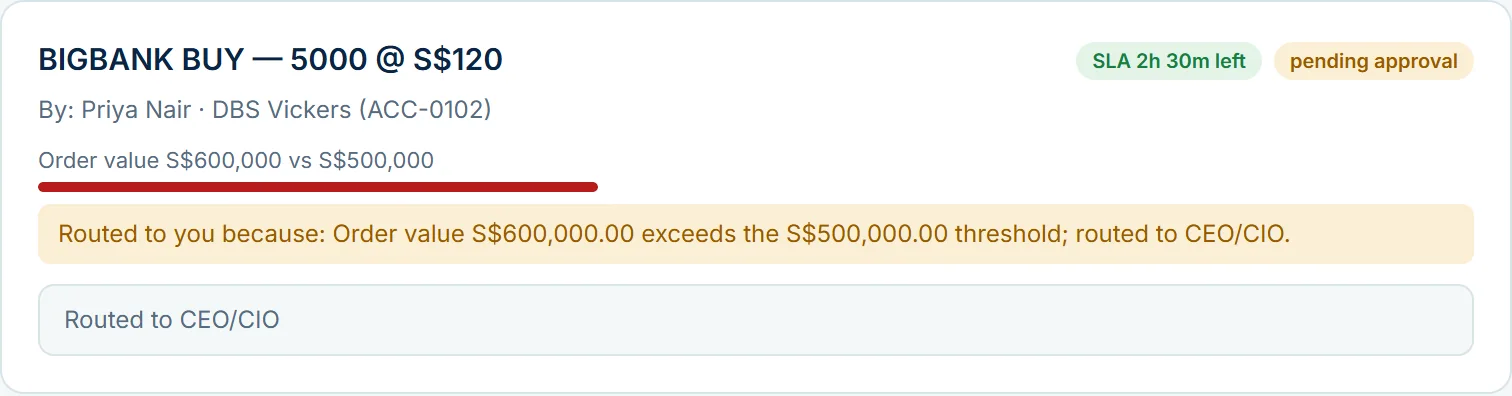
Reduce the work around compliance
Reduce the time and staff cost spent chasing replies, re-entering information and collecting evidence. Give your team more capacity for the reviews and decisions that need their judgement.
Reduce follow-up work
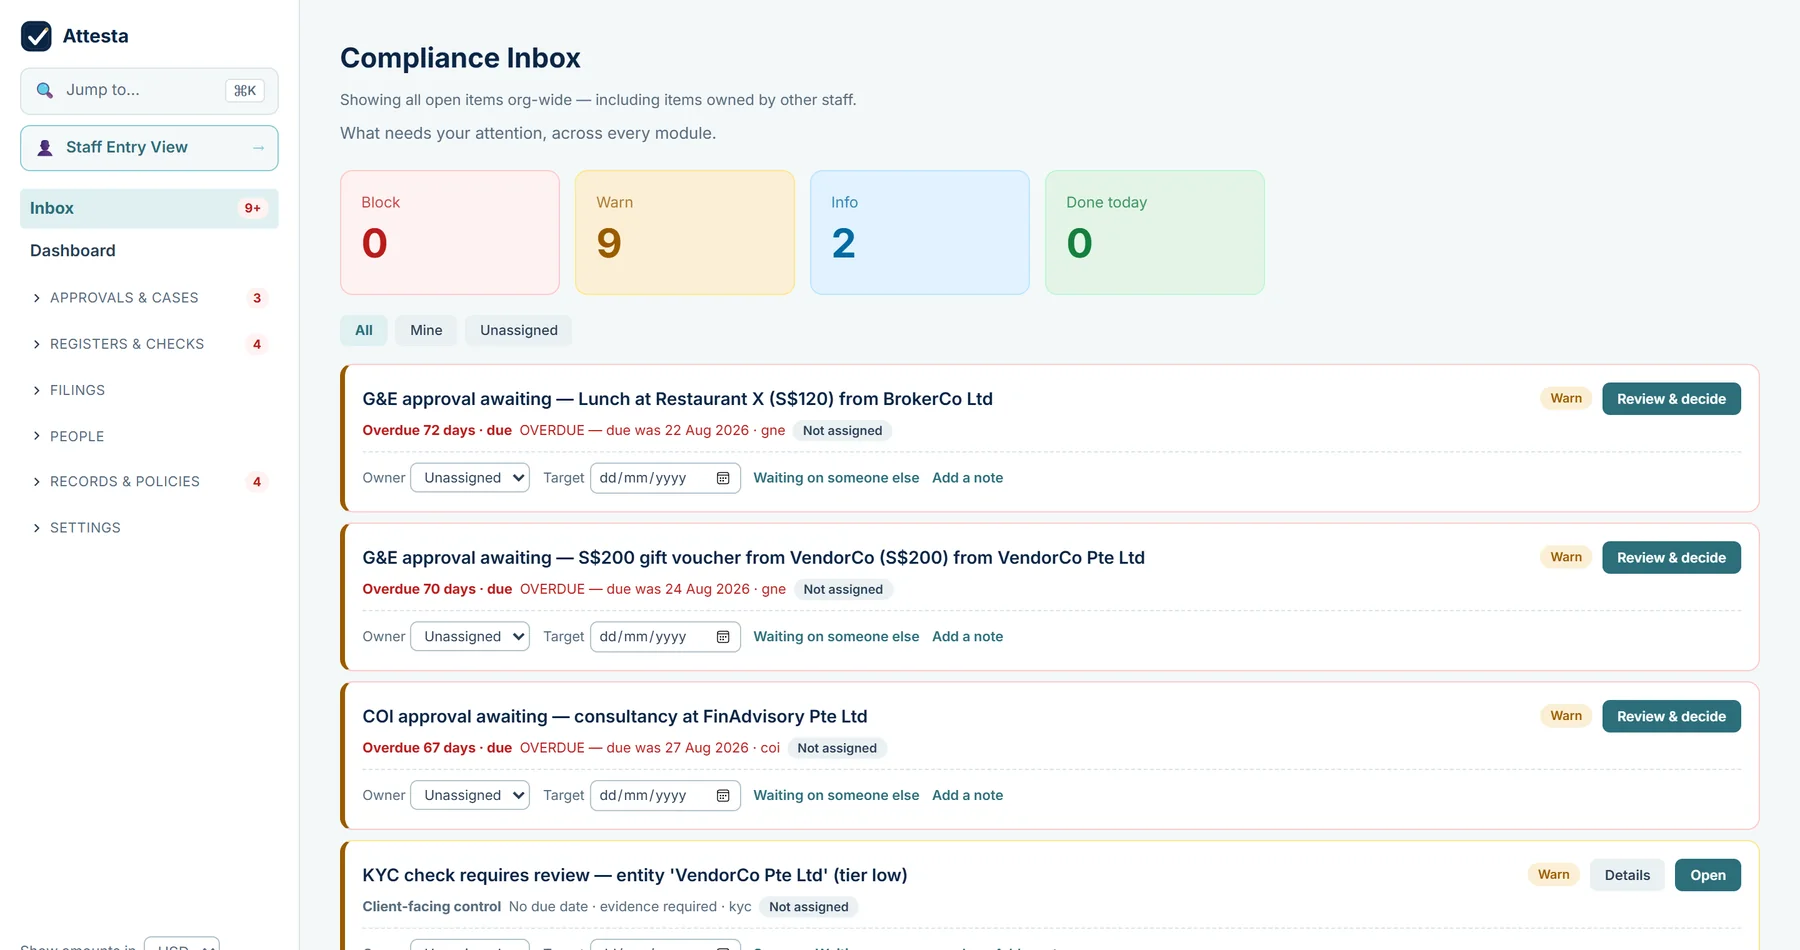
One list of what needs you, with an owner and a date, and a separate list of what you are waiting for.
Review with fewer hand-offs
The facts, the checks and the history are on the screen where the decision is made.
Prepare for audits as you work
Documents, decisions and reasons are kept together on the record they support.
Assign an owner, set a target date, add notes. Reminders pause while an item waits on another person.
Trade requests, gifts, outside interests and deal checks each show their evidence beside the decision.
Trade requests, gifts, outside interests and annual declarations are saved as people type.
Staff get a reference, the status and the next step as soon as they submit a trade request.
A PDF contract note fills in the execution details for the person to confirm, and stays on file as evidence. Manual entry is always available.
When something fails to load or a screening service is down, you see that, not a reassuring "all clear".
Import it, and Attesta proposes settings from its text for Compliance to review. Nothing changes until a person approves it.
One trade request, from an interrupted draft to filed evidence
An example with made-up names and figures, showing what each person sees.
Picks up where they left off
A request started before a meeting is still there, saved as they typed. They finish it and submit.
Gets a clear receipt
The receipt gives the reference, says the request is pending, and that they must not trade until it is approved.
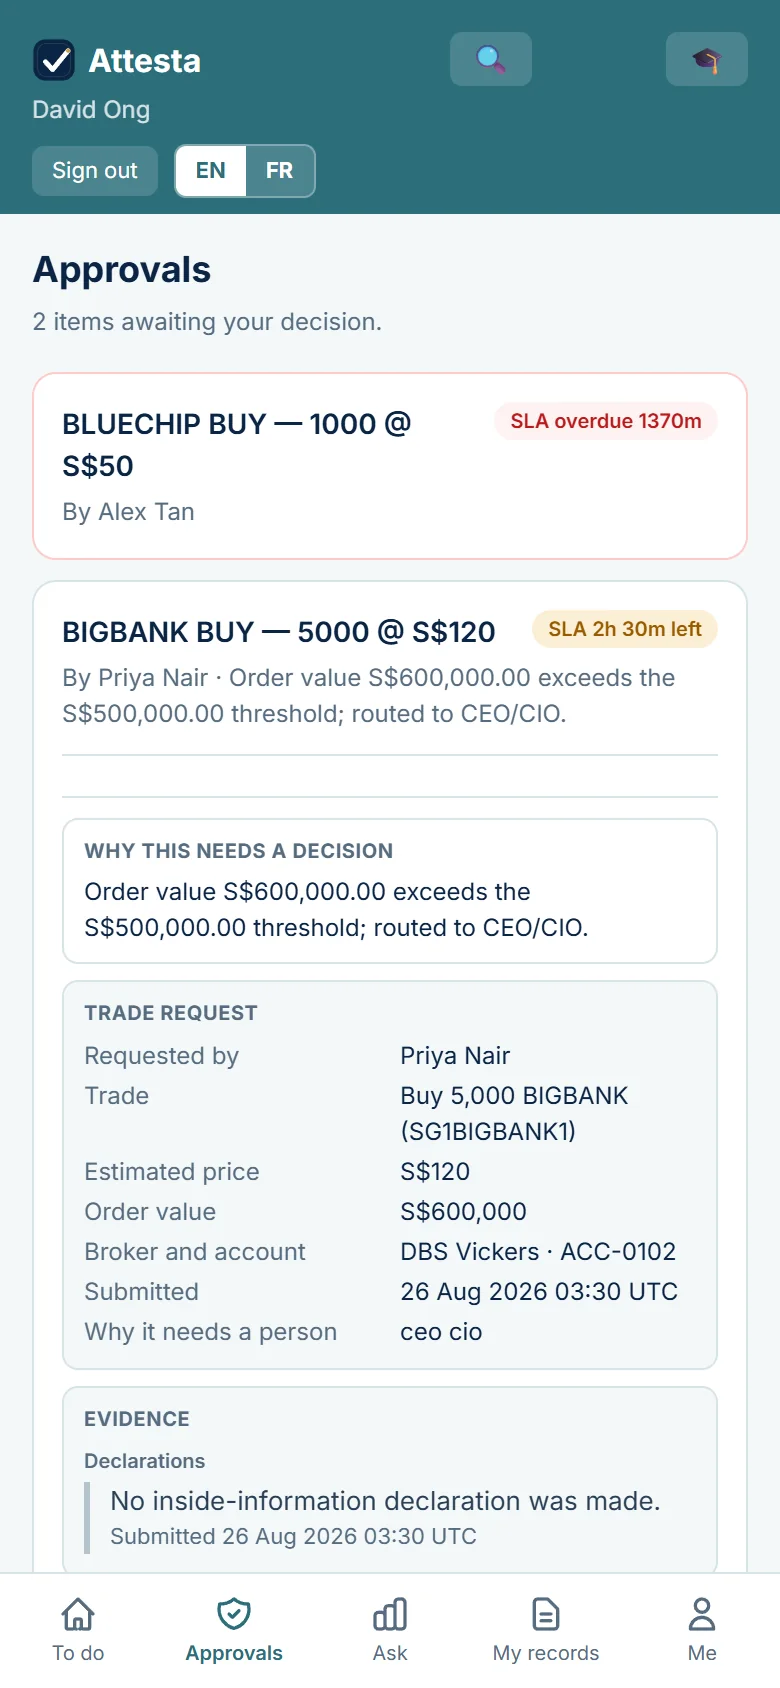
Decides with the facts in view
The checks, the limits that apply and the requester's recent trades in the same security sit beside the approve and reject buttons.
Reports the trade from the contract note
Attesta reads the broker's PDF contract note to fill in the execution report. The person checks it, and the note is kept as evidence.
Same firm, different front doors
Attesta does not hand everyone the same dashboard. Sign in and the product reshapes itself around what you are responsible for, on a desk or on a phone. Choose a role.
Auditors
Get the compliance screens read-only, with no staff view, because they do not file anything themselves, plus a list of their requests.
Compliance consultants and outsourced compliance officers
Work across the firms allocated to them, with a switch between one firm and all their firms, and a partner portal under their own brand. See compliance consultant software →
Screens captured from the current build with demonstration data in November 2026. Dates and overdue counts in the demonstration data are artefacts of how it was seeded.
Set to your firm, and to your regulator
Start with the workflows relevant to your firm. Our market pages explain the intended firm type, implemented features and current boundaries.
Singapore MAS
Fund-manager workflows
Explore scope →SFCHong Kong SFC
Fund-manager workflows
Explore scope →OSCCanada OSC / AMF
Ontario and Quebec • initial coverage
Explore scope →DFSADIFC DFSA
Initial coverage
Explore scope →ASICAustralia ASIC
Wholesale managers • initial coverage
Explore scope →SCMalaysia SC
Conventional managers • initial coverage
Explore scope →CIMACayman Islands CIMA
Regulated funds and directors
Explore scope →Canada, DIFC, Australia and Malaysia have initial implementation coverage available for scoped demonstrations. Local review and identified requirements remain outstanding. Availability of a preset does not mean every obligation is covered.
Compare an example workflow: Singapore, Hong Kong and Cayman
| Control | How Attesta applies it |
|---|
Regulatory requirements, guidance and configurable firm targets have different roles. Firm-policy targets can be configured; changing a setting does not change an applicable legal obligation. Confirm applicability during setup.
Explore the workflow modules
Five areas of daily compliance, each tied to the rule behind it
Where a workflow rests on a specific act, notice, code or guideline, the screen shows it, split into binding requirements and guidance.
Staff conduct
Before anyone trades, accepts a gift or takes an outside role.
- Personal dealing. Pre-clearance with automatic checks, holding periods, and contract notes matched as evidence.
- Conflicts. Annual declarations with last year's answers pre-filled, and outside interests scored for materiality.
- Gifts and entertainment. Thresholds by type, approval above them, one register.
People and competence
Who holds which role, and whether they are ready for it.
- Fit and proper. Annual review with declarations, evidence and a decision.
- Training. Hours tracked against the regulator's split, with reminders and escalation.
- Officer register. Appointments, changes and cessations open dated notification tasks; organisation charts saved with a fingerprint.
Financial crime
Know the client, and prove you checked.
- KYC and screening. Sanctions and politically exposed person checks, with a person confirming every possible match.
- Never falsely clear. If a screening service is down, the result says so instead of passing.
- AML governance. Risk assessment and audit cycles with sign-off.
Reporting and registers
The clocks that regulators set, watched for you.
- Misconduct and breaches. Cases start their statutory clock at discovery and open automatically from overdue items.
- Regulatory calendar. Every deadline with a reminder ladder and the filing reference recorded.
- Statutory registers and returns. Company registers and capital-return exports in Singapore; financial resources and annual return deadlines in Hong Kong.
Technology, data and speaking up
The controls examiners ask about second.
- Technology risk. Critical systems, cyber evidence, vendors, continuity tests and incident deadlines.
- Policies. Published to chosen roles, quizzed where the risk is high, with attestation tracked.
- Whistleblowing and complaints. Anonymous or named reports with a status reference; complaint clocks and resolution.
It is Monday. The regulator wants an answer by Friday. Pick the question.
Six questions firms are asked in inspections and board meetings, and what Attesta puts in front of you for each. Choose one.
Descriptions reflect the product as built in October 2026. Hong Kong document review is off by default and switched on by the firm; automatic clearance is off by default. Attesta records and checks; the firm decides, files and signs.
Show an examiner how it was decided, not only what was decided
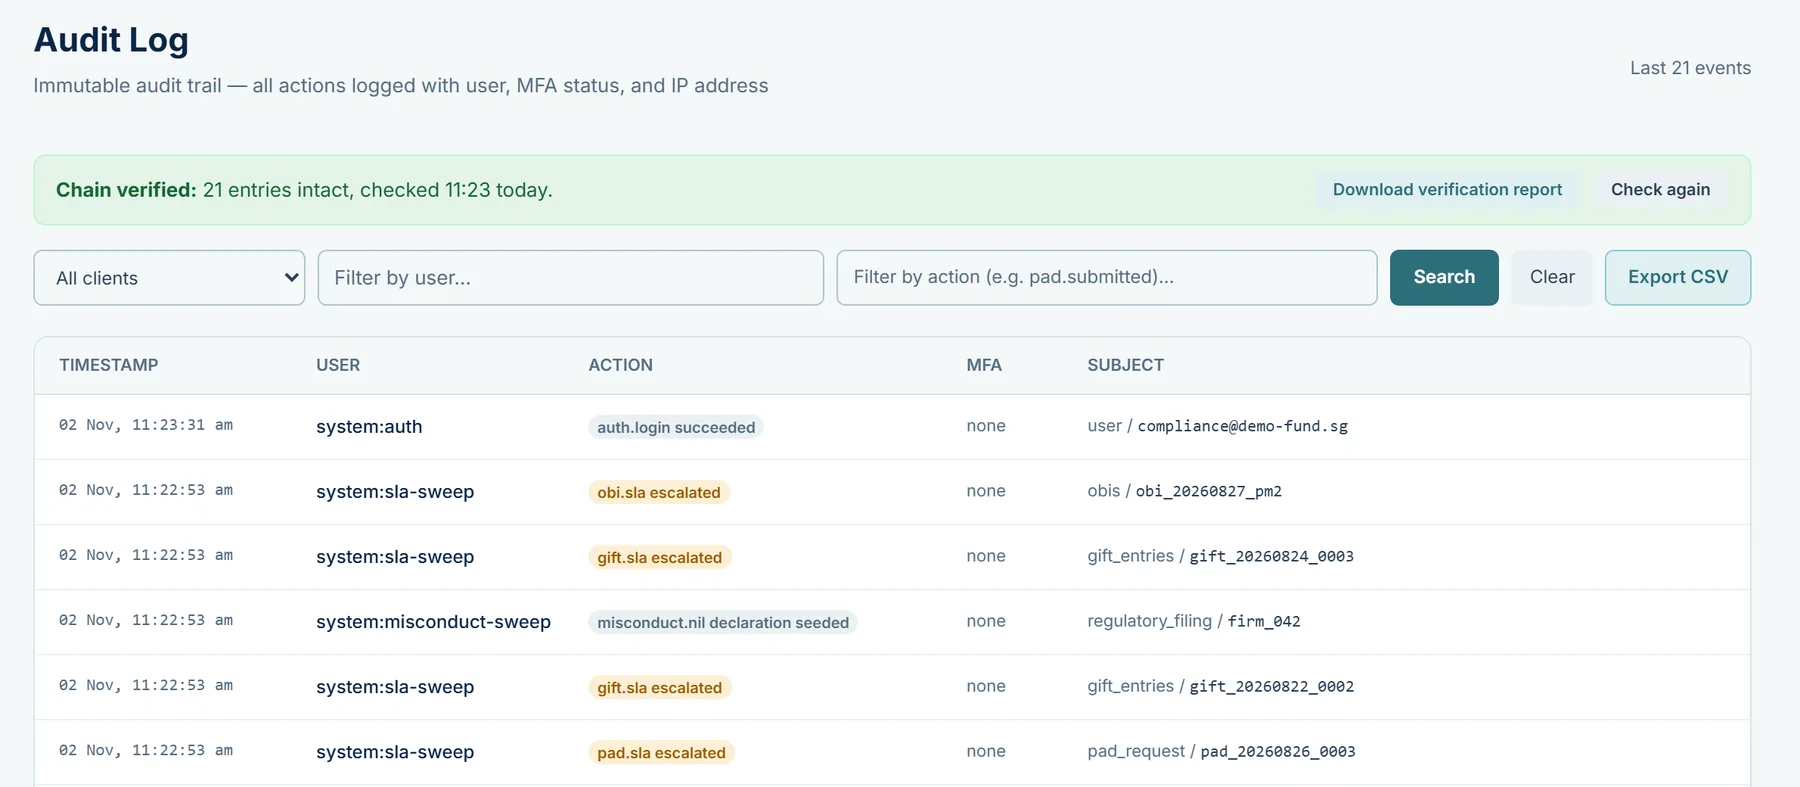
A tamper-evident audit trailEvery entry carries a fingerprint of the one before it. An integrity check shows where an entry inside the chain was changed or removed.
A second factor on designated approvals and privileged changesApprovals, screening dispositions, overrides and other privileged actions ask for it again, and record the method used.
Documents kept with the recordContract notes, certificates, minutes and filing acknowledgements are stored per firm and linked to what they support.
The integrity check detects edits and removals within the chain. As with any system log, the firm should still restrict database access and keep independent backups.
An illustration with made-up entries. The fingerprints are real SHA-256 values worked out in your browser: each entry is sealed with the one before it, so changing one shows up in the next.
What Attesta does, and what it leaves to you
Attesta does
- Turn rules into timed, approved, evidenced workflows.
- Remind, escalate, and open a breach case when a deadline is missed.
- Keep the audit trail and the supporting documents together.
- Show the regulatory basis on the workflows where a source applies.
The firm still does
- Make the decisions, and set thresholds that match its own policies.
- Submit filings to MAS, the SFC and other bodies. Attesta records the reference the firm obtains.
- Interpret a rule where it needs interpreting. Attesta is not legal advice.
Security design has been reviewed against ISO 27001 principles. The product is not certified to that standard.
See where your team can save time
Choose your market and tell us which work takes the most time. We will walk through approvals, follow-ups, data capture and evidence retrieval, then show how the workflows fit your firm. No client documents are needed to request a demo.
demo@attestacompliance.xyz